Sold via Gumroad
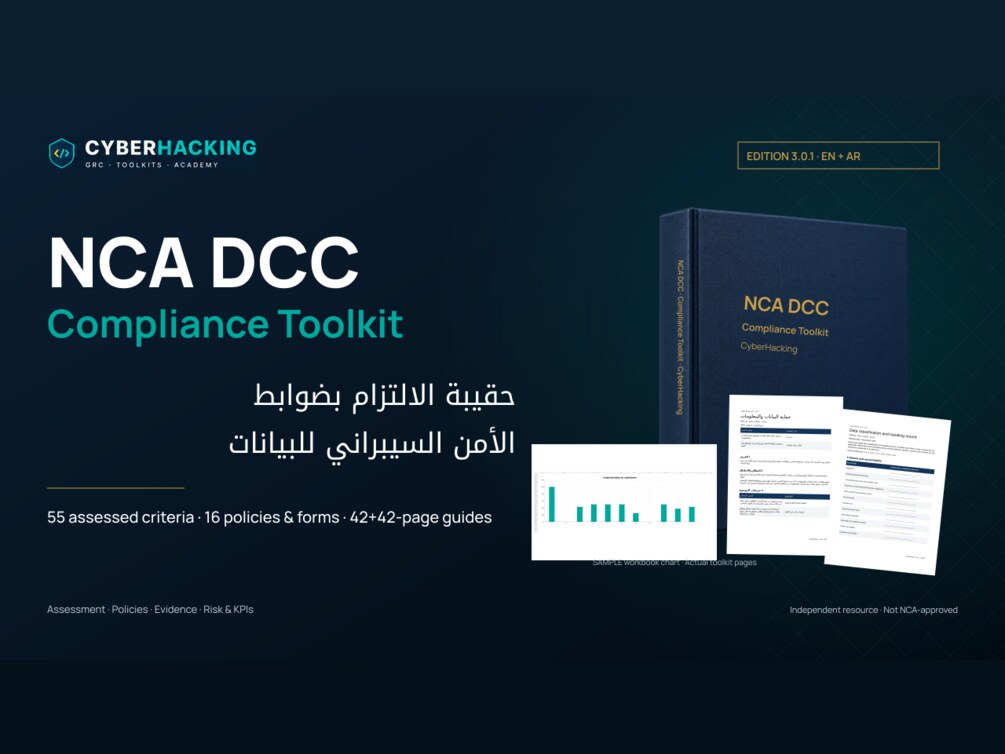
NCA CCC Compliance Toolkit v3.0 (Bilingual EN/AR)
Bilingual NCA CCC-2:2024 toolkit for CSPs and tenants: assessment workbook, risk register, 24 standards + 5 forms, guides and evidence samples. Licensed copy emailed within minutes.
New100% evidence coverage — every expected evidence item per control has a dedicated sample (Word documents, Excel registers and screenshot images) plus an Evidence Coverage Matrix.
- Evidence artifacts
- 82
- Evidence items mapped
- 341
- Coverage per control
- 100%
// Look inside
See what you get
A short preview video of this toolkit.
01
Overview
Turn cloud responsibility into controls you can operate and evidence you can verify: everything a cloud service provider (CSP) or cloud tenant (CST) in Saudi Arabia needs to assess, implement, evidence and sustain compliance with the NCA Cloud Cybersecurity Controls (CCC-2:2024): all 175 control records (135 independent assessment criteria) traced from requirement to standard, verification and evidence. Bilingual English + Arabic, fully editable. Built by a certified GRC practitioner (CISSP, CISM, CRISC, CISA).
02
What's inside (75+ files, English + Arabic)
Assessment Workbook (Excel, blank + filled SAMPLE)
Every CCC control with CSP/CST applicability and classification level, status, maturity score, evidence references, owner, reviewer and review date, with input validation. Live dashboard: implementation by official subdomain (EN/AR), implemented and assessed counts, internal maturity and chart. Control library with the official wording in English and Arabic, attributed to its source, plus framework mapping to ECC-2:2024, ISO/IEC 27001:2022, ISO/IEC 27017 and NIST CSF 2.0.
Risk & Remediation Register (Excel, blank + filled SAMPLE)
5x5 likelihood x impact method, CCC-linked risk register with inherent and residual scoring, remediation plan with owners and due dates, 48 KPI/KRI definitions with targets and RAG status, RACI matrix and source-based compliance calendar.
24 Standards + 5 Forms (Word, separate EN and AR editions)
Shared responsibility and authority, risk classification and acceptance, regulatory and contract assurance, personnel vetting and offboarding, production and emergency change, stack and tenant asset inventory, identity and privileged access, stack hardening and tenant isolation, network segmentation, administrative endpoints, data protection, portability and exit, cryptographic profiles and certificate trust, backup custody and recovery, vulnerability treatment and tenant notice, penetration testing, tenant audit trails and monitoring, incident response and tenant notification, facility access and disposal, application transaction integrity, key ownership and retrieval, secure development, storage media sanitation, secure continuity, and supply-chain assurance. 601 implementation statements per language citing the control IDs, adjustable settings, two six-step procedures per standard, measures and control verification annexes. Forms: CSP/CST cloud service assessment, data location and localization decision, portability, exit and disposal, privileged access and key retrieval, and incident tenant notice and custody. Coverage matrix (Excel) linking all 175 records.
Implementation Guides (PDF + DOCX, 57 pages EN / 57 pages AR)
Applicability for CSPs and CSTs, classification levels, the 2024 localization update, twelve-month roadmap and implementation by official subdomain.
Evidence Samples
Eight domain evidence books per language (175 learning cases, each with a positive example, an insufficient example and a verification workpaper) plus a bilingual Excel evidence index.
03
Executive Dashboard (board-ready)
- A one-page Executive Dashboard sheet in the assessment workbook: headline KPI tiles, compliance by domain and subdomain, and charts
- Every figure is calculated automatically from your assessment, so it updates the moment you change a status
- Drop it straight into a steering-committee or board pack; the separate risk dashboard shows inherent and residual risk at a glance
04
New 100% Evidence Coverage
Not sure what evidence an assessor will ask for? Every expected evidence item for every control now has a dedicated, realistic sample in 05-Evidence-Samples/Evidence-Artifacts.
- 82 evidence artifacts: 28 Word documents, 33 Excel registers and 21 screenshot images (consoles, dashboards, emails and diagrams)
- Examples: a shared responsibility matrix, security-zone firewall rules, tenant key-management standard revision history, a removable-media transfer log, log-archive WORM hashing configuration, test-data masking configuration and CCTV and guard patrol records
- Each sample carries a reference number, owner role, date, classification and an assessor verification note, so your team sees exactly what good evidence looks like
- Evidence Coverage Matrix (Excel): maps all 341 expected evidence items to the control they prove and to the sample that shows it
- These sit alongside the evidence books, so you get the explanation and a ready example for every control
05
What you receive
- One ZIP organised in numbered folders, ready to share with your team
- Blank workbooks for your own assessment plus filled SAMPLE versions to learn from
- Editable Word, Excel and PDF files in English and Arabic
- CHANGELOG and a release manifest with SHA-256 checksums for every file
06
Who it's for
Cloud service providers, cloud tenants, cybersecurity GRC, cloud architecture, internal audit and assurance teams at Saudi government entities, critical-infrastructure operators and regulated private organizations.
07
How delivery works
Your copy is individually licensed and watermarked with your name and order number, then emailed to you within minutes of purchase. One licence covers one legal entity. Consultants: contact support@cyberhacking.io for a multi-entity licence.
All sales are final. Faulty files are replaced when reported within 14 days to support@cyberhacking.io.
08
Disclaimer
Official NCA wording is attributed; standards, defaults and examples are implementation aids. This independent resource does not claim NCA approval, certification or endorsement.
09
Licence & usage
One licence covers one legal entity. Each copy is individually licensed and watermarked with the buyer's name.
// More toolkits